Cyber Data Solutions
Data intelligence for cybersecurity.
As the demand for data-driven threat intelligence grows, so does the complexity of data management at scale within constrained budgets.
When a SIEM is not enough.
Break the SIEM lock-in that drives detection gaps and high costs for enterprise SOCs. Infinitive enables detection engineers and threat hunters to keep using their existing SIEM while seamlessly adopting a scalable and cost-effective data lake for high-volume data sources and advanced analytics use cases.
By eliminating the need for rip-and-replace, our Cyber Data Solutions provide the flexibility needed for security leaders to confidently join the rest of the enterprise on the modern data stack without disrupting existing processes. Security operations teams at banks, airlines, and large tech companies use Infinitive’s Cyber Data Solutions to detect threats at scale and save millions of dollars.
Operational cybersecurity data challenges.
Data volume and diversity present several challenges to cyber analysts, data engineers, and others.
Data challenges
Data silos
Data stored across the enterprise and in various vendor systems is not easily integrated or shared, hampering a unified view of threats.
Heterogeneous data
Cyber analytics and monitoring consumes data from many non-standardized sources, with schemas that are prone to change.
Data governance at scale
Tracking lineage and managing access for numerous data sources in many use cases.
Maintaining hundreds of data pipelines
Ensuring data is ingested reliably and consistently from diverse sources feeding into centralized datastores.
Tool and analytics challenges
Swivel-chair analytics
Data needed to support investigations is often not in a centralized location for efficient or effective analysis.
SIEM alerts often lack context
Alerts sent to the SIEM from other security tools may lack proper context to be worked efficiently.
UBA tool limitations
User Behavioral Analytics (UBA) tools often lack historical search capabilities and transparency into potential threats.
Alert fatigue
The sheer number of alerts, often with many false positives, can overwhelm cyber analysts.
Cyber data lakehouse implementation.
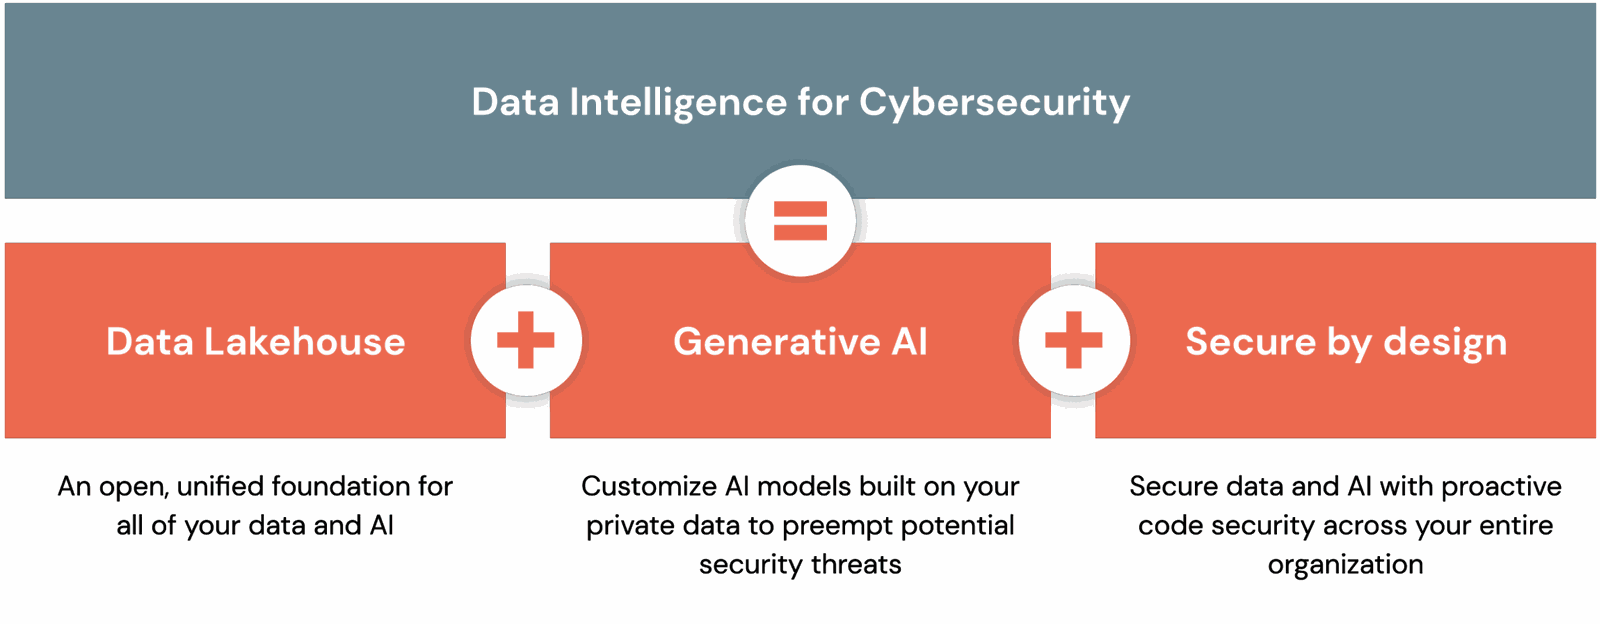
Implement a state-of-the-art Lakehouse architecture that combines the scalability of a data lake with the governance and transactional capabilities of a data warehouse. This unified platform supports advanced analytics and machine learning, providing a powerful yet cost-effective foundation for security operations.
SIEM augmentation
Enhance your SIEM’s capabilities and optimize storage costs via Databricks Delta Lake to efficiently analyze large volumes of data.
Real-time threat detection and incident response
Leverage the power of Databricks Lakehouse, streaming analytics, and automation to provide a robust solution for managing cybersecurity threats in real time.
Advanced vulnerability management and threat analytics
Proactively identify, assess, and remediate vulnerabilities by enabling analysts to conduct analysis of historical data at scale, and AI/ML for advanced predictive analytics.
Streamline threat detection and analysis.
The Databricks Data Intelligence Platform streamlines threat detection and analysis, while reducing costs and enhancing response accuracy.
- Reduced risk, complexity, and cost. Simplify the ingestion and retention of massive amounts of data, while reducing the complexity, noise, and costs typically associated with expanding datasets.
- Supports next-gen threat detection. Enable real-time insights and machine learning to identify the incidents that matter, helping to uncover hidden threat patterns and reducing false positives from SIEM tools.
- AI-powered security analytics. Facilitates the creation of machine learning models for faster and more accurate threat detection and response, streamlining the investigation and triage process across multiple data sources.
- Historic analysis at scale. Conduct extensive forensic analysis by enabling security teams to conduct thorough reviews of historical data and respond to incidents with increased precision and confidence.
- Multi-cloud, multi-region. Streamline threat detection while minimizing egress costs and adhering to data sovereignty regulations.
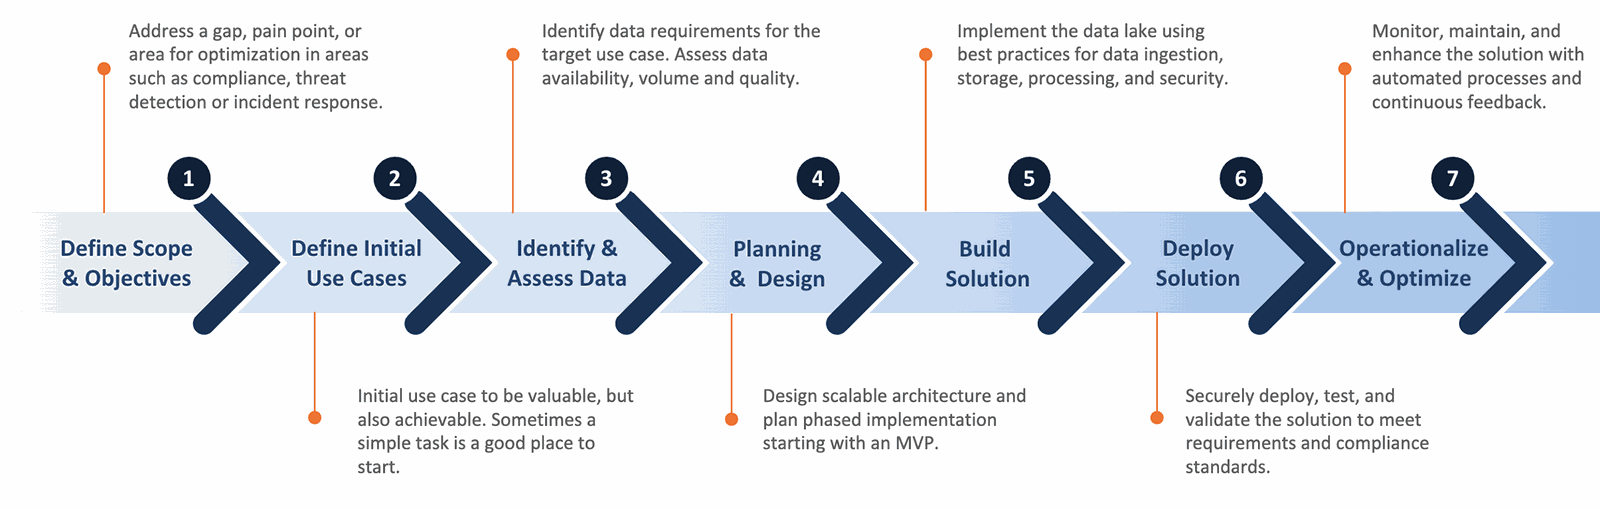
Infinitive’s cyber lakehouse development approach.
Infinitive’s Lakehouse development approach begins with clearly defining scope and priority use cases, followed by scoping and developing an achievable initial MVP solution.
Get started. Speak with a Databricks expert.
Bring your SIEM costs, data sources, and detection priorities. We’ll help scope a cyber lakehouse MVP that fits your security operations.